ISO Standards. Real Impact.
ISO 42001 Certification in Denver
Responsible AI. Stronger Governance. Greater Trust.
- IAS Accredited
- Independent Certification Body
- International Recognition
Your Certificate, Independently Verifiable
Every ISO/IEC 42001 certificate GMSQUEST issues is accredited by IAS and listed on the IAF CertSearch global register, where your customers can confirm it themselves.
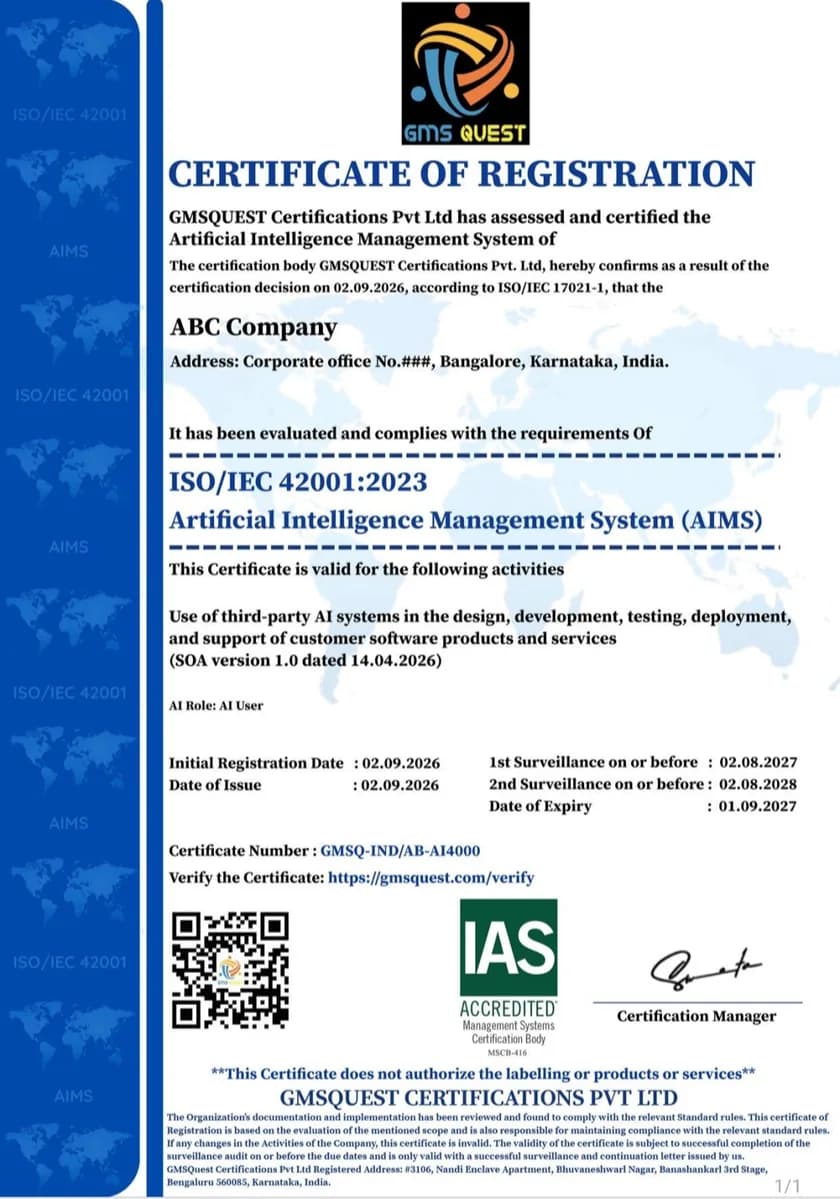
Sample certificate
What a GMSQUEST ISO/IEC 42001 certificate of registration looks like, including the IAS accreditation mark, the certificate number and the QR code that links to its record.
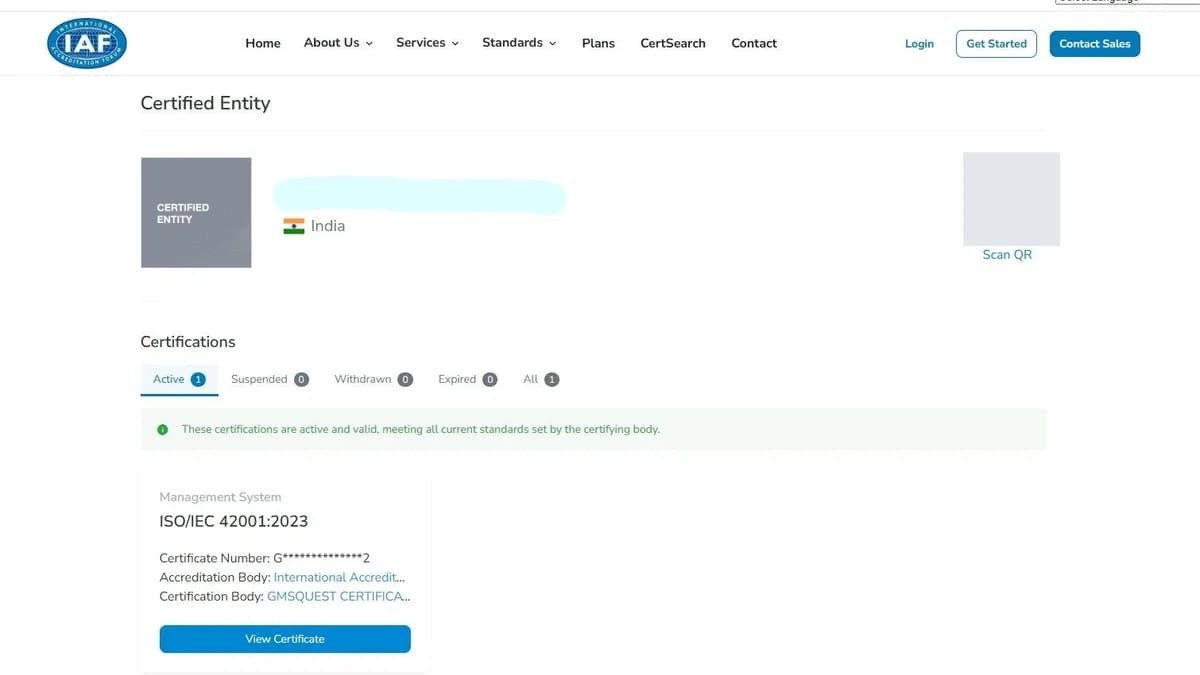
Listed on IAF CertSearch
GMSQUEST certificates appear on the International Accreditation Forum's global register. Anyone can search it and see the standard, the accreditation body and whether a certificate is active — without taking our word for it.
What is ISO 42001?
ISO/IEC 42001:2023 is an international management system standard specifically designed for organizations that develop, provide, or use artificial intelligence systems.
It establishes a systematic framework for managing AI-related governance, risks, impacts, processes, and responsibilities.
ISO/IEC 42001 can help organizations establish structured AI governance and demonstrate that their AI-related activities are managed through a defined and continually improving management system.
Why ISO 42001 Matters
AI introduces opportunities as well as specific governance, operational, ethical, and risk-management considerations. A management system approach helps organizations move from isolated AI controls and policies toward a structured framework with defined processes, responsibilities, objectives, monitoring, and continual improvement.
- Structured AI GovernanceEstablish processes, oversight, and responsibilities for managing AI-related activities.
- AI Risk & Impact ManagementCreate a systematic approach to identifying, assessing, and addressing AI-related risks and impacts.
- Transparency & AccountabilityDefine roles, policies, and management processes that support accountability for AI systems.
- Independent Conformity AssessmentCertification provides an external assessment of an AIMS against applicable ISO/IEC 42001 requirements.
- Stakeholder ConfidenceAn internationally recognized management system standard can help communicate an organization's structured approach to AI management.
What ISO 42001 Certification Delivers
An implemented Artificial Intelligence Management System can provide a structured basis for:
- AI governance policies and objectives
- Defined responsibilities and accountability
- AI risk and impact assessment processes
- Management oversight and operational controls
- Monitoring, corrective action, and continual improvement
- Demonstration of conformity with ISO/IEC 42001
ISO 42001 Certification for Denver Organizations
Denver, Colorado, is a regional business and technology center serving industries such as software and information technology, aerospace, telecommunications, energy, healthcare, financial services, professional services, and advanced manufacturing.
Organizations across the Denver metro area may use AI for forecasting, customer support, cybersecurity, document processing, operational analytics, resource planning, and decision support. As these applications grow, organizations need clear ownership, risk assessment, and consistent oversight of AI-related activities.
ISO/IEC 42001:2023 specifies requirements for an Artificial Intelligence Management System (AIMS). It provides a management-system framework for establishing, implementing, maintaining, and continually improving processes for AI governance, risk and impact assessment, accountability, and oversight.
GMSQUEST lists ISO/IEC 42001:2023 among its certification scopes and describes its role as an independent, impartial third-party management-system certification body. Denver-area organizations can evaluate whether an AIMS is appropriate for the AI systems they develop, provide, integrate, or use.
AI in Denver
Denver’s wider business ecosystem includes technology and software firms, aerospace and satellite businesses, energy companies, healthcare organizations, financial services, telecommunications, logistics, and public-sector suppliers.
Potential AI use cases include software development support, anomaly detection, energy-demand forecasting, predictive maintenance, cybersecurity analysis, customer-service automation, clinical or administrative workflow support, and supply-chain planning.
ISO/IEC 42001 can help organizations define AI governance roles, establish policies, assess AI-related risks and impacts, document controls, monitor system performance, and improve processes over time. A structured AIMS can also support customer due diligence, supplier assessments, internal accountability, and discussions with business partners about how AI is governed.
The standard may be relevant to organizations that develop, provide, integrate, or use AI systems. Certification scope should reflect the organization’s actual activities, AI systems, and management-system boundaries. ISO/IEC 42001 is a management-system standard; certification does not independently certify every AI product or guarantee that a system is safe, unbiased, secure, or error-free.
Regulatory & Market Context
Organizations operating in Denver may need to consider Colorado law, applicable federal requirements, sector-specific rules, contracts, and customer expectations. The obligations that apply depend on the organization’s industry, the personal or sensitive data it handles, its role in the AI lifecycle, and the decisions supported by AI.
• Colorado Privacy Act: Organizations that meet the law’s applicability thresholds should assess obligations concerning personal data, consumer rights, data protection assessments, and profiling. Applicability depends on the organization and processing activities.
• Colorado AI legislation: Colorado has enacted legislation addressing certain high-risk AI systems and algorithmic discrimination, commonly associated with SB 24-205 (the Colorado AI Act). Because effective dates, amendments, and implementation details can change, verify the current statutory text and requirements before making legal claims or publishing compliance promises.
• Healthcare and health technology: Healthcare providers, vendors, and health-tech organizations should determine whether HIPAA and other applicable privacy, security, clinical, research, or contractual requirements apply to their AI-enabled workflows.
• Aerospace, energy, and critical operations: Organizations using AI in aerospace, energy, infrastructure, or safety-sensitive operations should assess applicable sector regulations, cybersecurity obligations, safety controls, supplier requirements, and contractual commitments.
• Employment and automated decisions: Employers using AI in recruitment, screening, evaluation, or other employment-related decisions should review applicable employment, anti-discrimination, privacy, and consumer-protection requirements and consider appropriate human oversight.
• Federal and sector-specific requirements: Depending on the activity, organizations may need to consider federal privacy, consumer-protection, cybersecurity, financial-services, healthcare, or procurement requirements. ISO/IEC 42001 does not replace these obligations.
• AI risk-management practices: The NIST AI Risk Management Framework can serve as a voluntary reference for organizing AI risk work. ISO/IEC 42001 provides a management-system framework; neither replaces legal advice or a review of requirements that apply to a particular use case.
• Procurement and stakeholder assurance: Customers and enterprise buyers may ask how AI risks are identified, responsibilities assigned, systems monitored, and corrective actions managed. A documented AIMS can provide a consistent basis for responding to these questions.
ISO/IEC 42001 certification does not automatically establish compliance with every law, regulation, contract, or sector-specific requirement. Organizations should consult qualified legal advisers and verify current requirements for their own circumstances.
Industries Served in Denver
Organizations across these sectors may be within the scope of ISO 42001, depending on their AI activities and certification scope.
- Technology & Software
- Telecommunications
- Financial Services
- Healthcare & Life Sciences
- Manufacturing
- Professional Services
- Education
- Other
Why Choose GMSQUEST?
Independent, impartial third-party certification for ISO 42001 in Denver.
- Independent Third-Party CertificationGMSQUEST operates as an independent certification body and conducts third-party management system certification rather than consultancy or implementation services.
- IAS Accredited Certification BodyAccredited by the International Accreditation Service as a Management System Certification Body, with ISO/IEC 42001:2023 within its accredited scope.
- Impartial CertificationCertification activities are conducted according to principles of impartiality, competence, confidentiality, and transparency, with certification decisions based on objective evidence.
- Qualified Auditors & Technical ExpertiseGMSQUEST works with qualified auditors and technical experts to deliver management system certification services.
- Transparent Certification ProcessFrom application and Stage 1 through Stage 2, certification decision, surveillance, and recertification, the process is structured with defined stages and reporting.
Certification Process
- 01Application SubmissionSubmit your organization details, intended certification scope, and relevant information.
- 02Application & Agreement ReviewThe submitted information is reviewed for completeness, scope clarity, and certification feasibility.
- 03Audit Programme & QuotationAudit duration, planning, and the commercial proposal are prepared based on the reviewed information.
- 04Stage 1 AuditThe organization's management system documentation and preparedness are reviewed.
- 05Stage 2 AuditThe implementation and effectiveness of the Artificial Intelligence Management System are assessed against the applicable requirements.
- 06Certification DecisionAudit results and applicable corrective actions are reviewed before an independent certification decision is made.
- 07Surveillance & RecertificationPeriodic surveillance audits are conducted to maintain certification, followed by recertification according to the applicable certification cycle.
Accreditation
Management System Certification Body
- Standard
- ISO/IEC 17021-1:2015
- Accreditation number
- MSCB-416
GMSQUEST Certifications Private Limited is accredited by the International Accreditation Service as a Management System Certification Body (MSCB-416). Certifications issued prior to 17 August 2026 were issued before accreditation and are not accredited.
View our accreditation certificateOther Locations
The same accredited certification, elsewhere.
Get in Touch
Fill out the form and our certification team will get back to you.
Talk to Our Certification Team
- Phone+1 855 848 2951US/Canada — call or leave a voicemail
- WhatsApp+917353432833
- Emailinfo@gmsquest.com
- LinkedInlinkedin.com/in/gmsquestgopinath
Contact GMSQUEST to confirm current geographic service availability and certification arrangements. Enquiries are answered from our office in Bengaluru, India (UTC+5:30).